Product launches
New products, and expansions of existing ones.
Product launch
Artemis Security launches Detection as Code feature
Detection rules integrate into customer GitHub, GitLab, Bitbucket Cloud, or Cursor Origin repositories via automated pull requests.
 Artemis Security
· 15 Oct 2026 · 1 source · Vendor sources only
Product launch
Trellix Redefines Cyber Defense for the AI Era
Trellix launched Trellix Wise for Private Cloud, the first on-premises federated AI core for security operations centers, designed to deliver machine-speed cyber defense for data-sensitive environments.
 Trellix
· 14 Oct 2026 · 4 sources · Reported by multiple independent sources
Product launch
Arctic Wolf launches SwarmView for AI investigation visibility
SwarmView gives customers visibility into AI-driven investigations, launched at 2026 Security Operations Summit.
 Arctic Wolf
· 14 Oct 2026 · 4 sources · Also reported independently

Product launch
Arctic Wolf launches Aurora Superintelligence Platform and Agentic SOC
The platform and Agentic SOC help organizations understand and secure AI decision-making in cyber defense.
Arctic Wolf · 14 Oct 2026 · 2 sources · Vendor sources only
Product launch
Backline launches feature routing remediation tickets to individuals
The feature automatically routes security remediation tickets to specific individuals, integrating with Slack, Teams, and Jira.
 Backline AI
· 14 Oct 2026 · 1 source · Vendor sources only
Product launch
Elastic launches Context Engine, nightshift and AlertZero AI tools
Context Engine provides AI agents enterprise context; nightshift adds AI SRE incident response; AlertZero automates alert triage and threat hunting.
 Elastic
· 14 Oct 2026 · 1 source · Vendor sources only

Product launch
Crogl releases version 2.12.1 with faster triage and new connectors
Adds Claude 5 and GPT-6 support, Darktrace connector, deeper Microsoft Sentinel integration, scheduled jobs, exports, and Kubernetes deployment.
 Crogl
· 13 Oct 2026 · 1 source · Vendor sources only
Product launch
Dropzone AI launches hunt packs for parallel threat hunting
Hunt packs let AI threat hunting agents run five to ten hunts simultaneously, giving analysts a head start.
 Dropzone AI
· 13 Oct 2026 · 1 source · Vendor sources only
Product launch
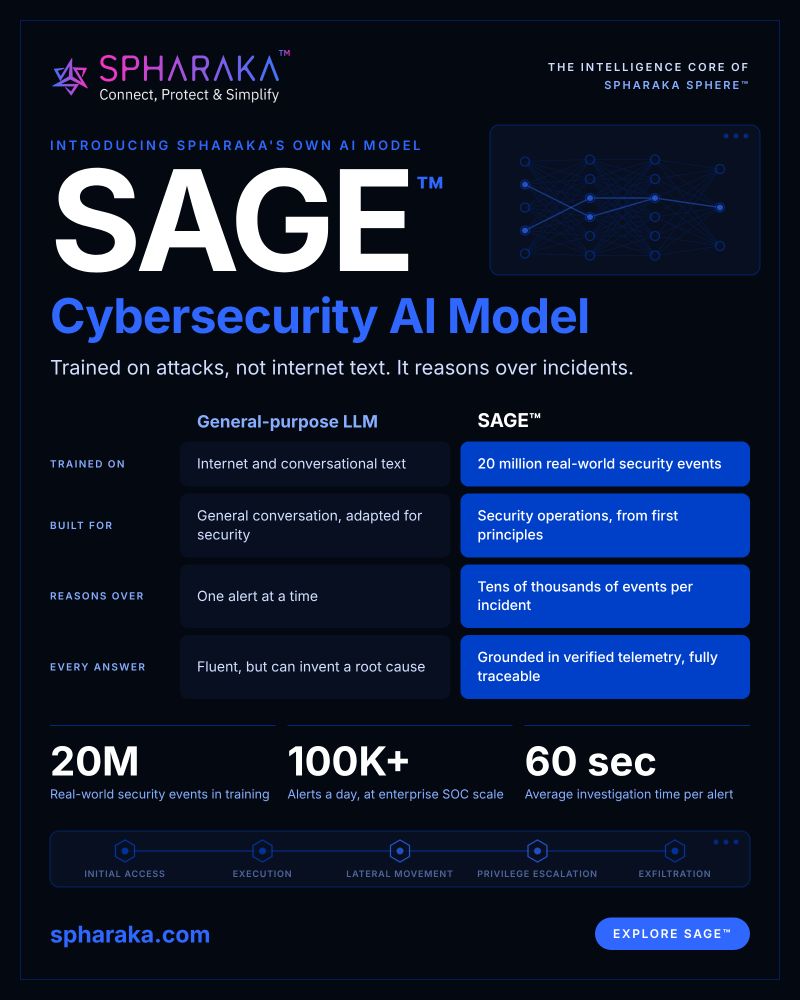
Spharaka launches SAGE, a cybersecurity-trained AI model
SAGE is trained on 20 million real-world security events and reasons over tens of thousands of events per incident.
 Spharaka
· 13 Oct 2026 · 1 source · Vendor sources only

Product launch
Torq launches REV channel partner program for AI SOC
Torq REV offers partners 100% services margin protection, full channel ownership, and a 10-day path to selling.
 Torq
· 13 Oct 2026 · 1 source · Vendor sources only

Product expansion
Cotool adds Opus 5.5, GPT-6 Sol, GPT-6 Luna to model catalog
Cotool released new models to its catalog alongside sandbox network restrictions, escalation visibility and delivery resend capability.
 Cotool
· 12 Oct 2026 · 1 source · Vendor sources only
Product launch
Imperum launches Cognitio threat actor intelligence capability
Cognitio connects adversary profiles, cross-vendor aliases, MITRE ATT&CK techniques, vulnerabilities and advisories to SOC workflows.
 Imperum
· 12 Oct 2026 · 1 source · Vendor sources only
Product launch
Microsoft puts Azure Maia 200 AI chip into production
Microsoft announces Azure Maia 200 is now in production, with plans to scale to multi-gigawatt deployments by 2027.
 Microsoft
· 12 Oct 2026 · 1 source · Vendor sources only

Product launch
Splunk ships Enterprise Security 8.7
New release adds governed response, stronger automation and connected security context.
Splunk · 12 Oct 2026 · 1 source · Vendor sources only
Product launch
Rapid7 releases Metasploit Framework 6.5.6
Includes 12 new modules targeting LLMs, Linux privilege escalations, and Windows AARCH64 payloads.
 Rapid7
· 9 Oct 2026 · 1 source · Vendor sources only
Product launch
Artemis Security launches Orion-1 frontier model for cyber defense
The company claims it is top performer on its new Decision-Grade Readiness benchmark measuring trustworthiness of security decisions.
Artemis Security · 8 Oct 2026 · 4 sources · Reported by multiple independent sources
Product launch
Elastic’s AlertZero puts AI agents to work on security alert overload
Elastic N.V. launched AlertZero, AI agents for security operations that automate alert triage, threat hunting, and forensic analysis within Elastic Security, with customizable human oversight levels.
Elastic · 8 Oct 2026 · 2 sources · Reported by multiple independent sources
Product expansion
Elastic launches nightshift AI SRE in private preview
The AI SRE investigates alerts, finds unknown issues, recommends fixes, and works from Kibana, terminal or user-chosen agent.
Elastic · 8 Oct 2026 · 1 source · Vendor sources only
Product launch
Bricklayer AI launches Agentic Approvals for security action workflows
The system enables automated containment of threats like compromised workstations after meeting defined criteria.
 Bricklayer AI
· 8 Oct 2026 · 2 sources · Vendor sources only
Product launch
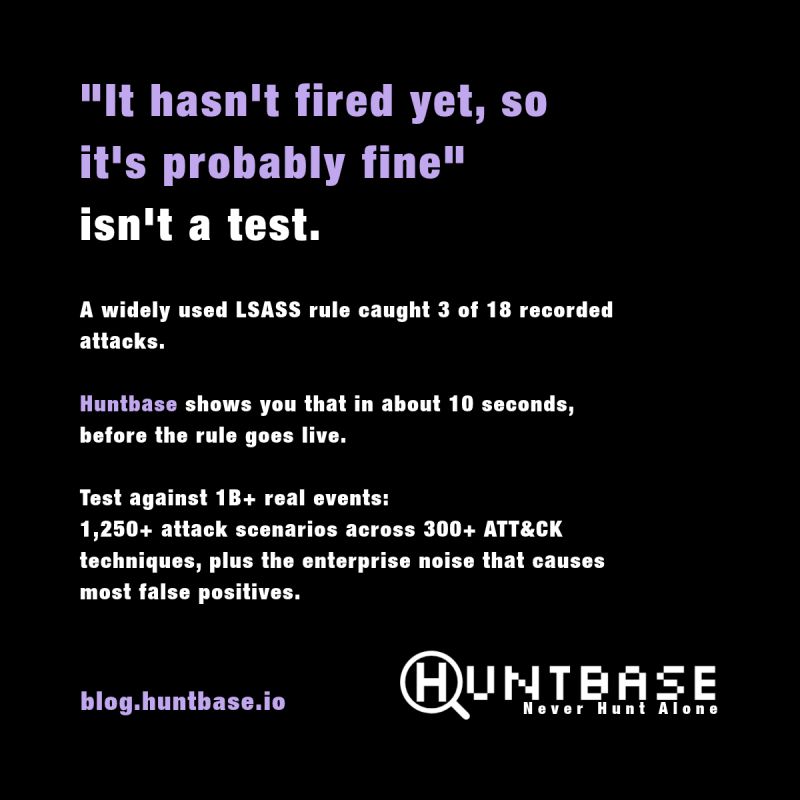
Huntbase launches test lake with 1,250+ recorded attacks
Test lake offers 1,250+ recorded attacks, 300+ MITRE techniques, 1B+ events, rule testing in ~10 seconds.
 Huntbase
· 8 Oct 2026 · 2 sources · Vendor sources only
Product launch
Simbian launches AI SIEM to augment existing SIEM infrastructure
The solution queries data in place and writes AI-generated verdicts back to incidents without SIEM replacement.
 Simbian
· 7 Oct 2026 · 1 source · Vendor sources only
Product expansion
NextSOC launches agentic security operations platform
AI agents investigate and respond across identity, endpoint, cloud, network, email and SaaS without replacing existing stack.
 NextSOC
· 6 Oct 2026 · 1 source · Vendor sources only

Product launch
Splunk launches Agent Observability capabilities for AI agents
New capabilities track AI token usage, monitor agent behavior, and connect AI adoption to business value.
Splunk · 6 Oct 2026 · 1 source · Vendor sources only
Product expansion
Stellar Cyber releases 7.0 with AI case triage and APIs
Stellar Cyber 7.0 unifies AI-powered case triage, SOC workflows, investigative evidence, automated response and new APIs.
 Stellar Cyber
· 5 Oct 2026 · 5 sources · Reported by multiple independent sources

Product expansion
Arctic Wolf adds 13 new integrations to Aurora Superintelligence Platform
New integrations include Cloudflare WAF, Claroty xDome Healthcare and Industrial, ExtraHop, Imperva WAF, Google Workspace, Veeam, Epic, and 1Password.
Arctic Wolf · 5 Oct 2026 · 1 source · Vendor sources only
Product expansion
Intezer revenue triples as enterprise AI security expands
Intezer reported tripled revenue as enterprises deploy AI security tools in live operations, driven by staffing shortages and SOC alert overload pushing automation adoption.
 Intezer
· 2 Oct 2026 · 1 source · Also reported independently
Product launch
Splunk introduces new Agentic SOC capabilities at SplunkConf26
Capabilities help organizations move faster from signal to action with trusted context, governance and automation.
Splunk · 2 Oct 2026 · 2 sources · Also reported independently
Product launch
Rapid7 launches Rapid7 Intelligence, unified threat intel and vulnerability engine
Built on Metasploit and Labs foundation, it monitors threats in real time.
Rapid7 · 2 Oct 2026 · 1 source · Vendor sources only
Product launch
Exabeam releases October 2026 New-Scale platform update
Adds AI-assisted investigation, agent activity visibility, improved reporting and governance with behavioral baselines.
 Exabeam
· 1 Oct 2026 · 8 sources · Reported by multiple independent sources
Product launch
Exabeam adds Agentic SOC capabilities to New-Scale platform
Update addresses autonomous digital workers using legitimate credentials and faster threat investigation.
Exabeam · 1 Oct 2026 · 3 sources · Also reported independently
Product launch
Palo Alto Networks launches Cortex XCOR AI-driven observability platform
Features autonomous response capabilities with AI SRE.
 Palo Alto Networks
· 1 Oct 2026 · 2 sources · Vendor sources only

Product launch
Splunk Observability innovations announced at SplunkConf26
Designed to help teams evaluate agent behavior, understand token usage, and troubleshoot faster.
Splunk · 1 Oct 2026 · 2 sources · Vendor sources only

Product launch
Cylerian's Cyra agent automates platform tasks via chat
Cyra builds client reports and executes scoped actions like isolation or credential reset through conversational sessions.
 Cylerian
· 1 Oct 2026 · 1 source · Vendor sources only
Product launch
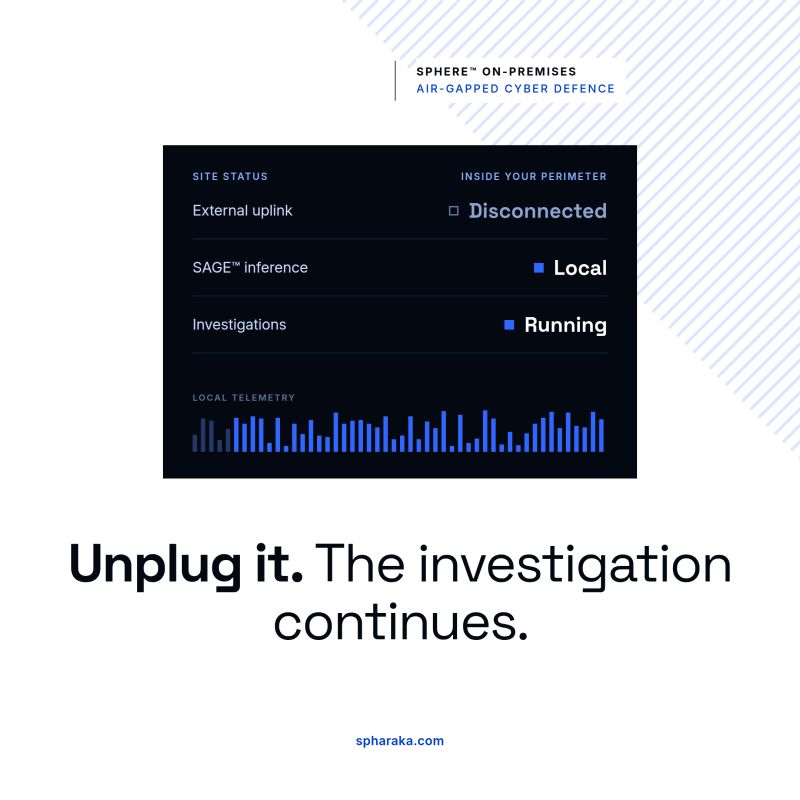
Spharaka launches Sphere On-Premises with local AI reasoning
SAGE and AuraXP agents run fully air-gapped with 60-120 second investigations.
Spharaka · 1 Oct 2026 · 1 source · Vendor sources only
Product launch
Splunk releases Cloud Platform 10.6 and Enterprise 10.6
New versions bring more ways to analyze data where it lives, put AI assistance into investigations and simplify platform operations.
Splunk · 1 Oct 2026 · 1 source · Vendor sources only
Product launch
Google introduces Gemini 4 Argon frontier intelligence model
Offers 1M token output limit for engineering, knowledge work and cybersecurity; rolling out to defenders via Fairwind Program.
Google SecOps · 30 Sep 2026 · 2 sources · Vendor sources only
Product launch
UnderDefense introduces MAXI MCP security platform
Enables organizations to retain SIEM data lake while offering AI SOC capabilities, with on-premise deployment for data sovereignty.
 UnderDefense
· 30 Sep 2026 · 2 sources · Vendor sources only
Product launch
Anvilogic launches Enterprise Security Graph for SOC AI agents
The graph integrates detections, feeds, alerts and historical decisions to reduce cold-start problems for AI agents.
 Anvilogic
· 30 Sep 2026 · 1 source · Vendor sources only
Product launch
Huntbase launches with 152 hunts, now 207
Self-service threat hunting library with reviewed hunts, growing from 152 to 207 hunts in six days.
Huntbase · 30 Sep 2026 · 1 source · Vendor sources only

Product launch
Mars Security launches Alert Hunts for cross-tool alert investigation
Investigates alerts across all connected sources with verdict, MITRE mapping, evidence log; no new pipeline needed.
 Mars Security
· 30 Sep 2026 · 1 source · Vendor sources only

Product launch
Splunk releases AI Assistant v2 with Agent Mode
New version can take action with Agent Mode, find content with Semantic Search, and learn naming conventions with Teach AI.
Splunk · 30 Sep 2026 · 1 source · Vendor sources only

Product launch
Beacon Security integrates with Claude's Compliance API
The integration is available today.
 Beacon Security
· 29 Sep 2026 · 1 source · Vendor sources only
Product launch
Cantina launches The Brain, shared memory for its agents
The Brain connects identities, devices, repositories and cloud services with operating context and prior investigations.
 Cantina
· 29 Sep 2026 · 1 source · Vendor sources only
Product launch
IBM and Yotta launch sovereign agentic AI platform for Indian organizations
The platform became generally available September 29, 2026, enabling data-resident AI capabilities.
 IBM
· 29 Sep 2026 · 1 source · Vendor sources only
Product launch
SentinelOne launches Claude Compliance API integration for prompt security
SentinelOne Prompt Security enforces policy on Claude prompts in real time, agentless.
 SentinelOne
· 29 Sep 2026 · 1 source · Vendor sources only
Product launch
Nebulock releases open-source GATES Method framework
Nebulock's GATES Method, built with its detection team, helps decide when to promote threat hunts to detections; open source.
 Nebulock
· 28 Sep 2026 · 4 sources · Vendor sources only

Product launch
AiStrike launches AiStrike for Insider Threat
The product autonomously investigates behavioral anomalies and drives governed response across identity, endpoint, cloud, DLP and physical access.
 AiStrike
· 28 Sep 2026 · 1 source · Vendor sources only
Product expansion
SentinelOne extends Wayfinder coverage across endpoints, identities, and cloud workloads
SentinelOne · 25 Sep 2026 · 1 source · Also reported independently
Product launch
Microsoft launches reimagined Copilot with Home, Code and Autopilot capabilities
The platform connects existing tools with AI features for building and scaling solutions.
Microsoft · 25 Sep 2026 · 2 sources · Also reported independently
Product launch
VigilBase launches VigilBase Platform for unified tool management
The VigilBase Platform unifies tools teams already pay for into one platform for visibility and control.
 VigilBase
· 25 Sep 2026 · 1 source · Vendor sources only
Product expansion
Strike48 launches on-prem agentic SOC appliance for air-gapped deployments
Industry-first appliance for on-prem and air-gapped deployments with local inference, supporting four deployment models including fully air-gapped.
Strike48 · 23 Sep 2026 · 2 sources · Also reported independently
Product expansion
Inside CrowdStrike’s Move To Secure Enterprise Agentic AI
CrowdStrike expands its Falcon platform to secure AI agents, creating new revenue opportunities across endpoint protection, identity management, cloud security, and its agentic security operations center.
 CrowdStrike
· 23 Sep 2026 · 1 source · Also reported independently

Product expansion
BlinkOps integrates with Microsoft Sentinel Data Lake
Direct connection brings Sentinel data into agentic security operations for investigations and response.
 BlinkOps
· 23 Sep 2026 · 1 source · Vendor sources only
Product launch
Huntbase opens self-service access to threat hunting platform
Users can now sign up and run hunts without prior request; platform grew from 149 to 162 hunts.
Huntbase · 22 Sep 2026 · 2 sources · Vendor sources only

Product launch
Spectrum Security launches Detection Health to find broken rules
Continuously checks every detection against live environment, identifies root cause, and generates customized fixes with human in the loop.
 Spectrum Security
· 22 Sep 2026 · 1 source · Vendor sources only
Product expansion
Exaforce introduced Agentless AI Security for AI agent visibility and control
The product discovers AI agents, analyzes risk and permissions, and protects sensitive data across environments.
 Exaforce
· 17 Sep 2026 · 1 source · Vendor sources only
Product launch
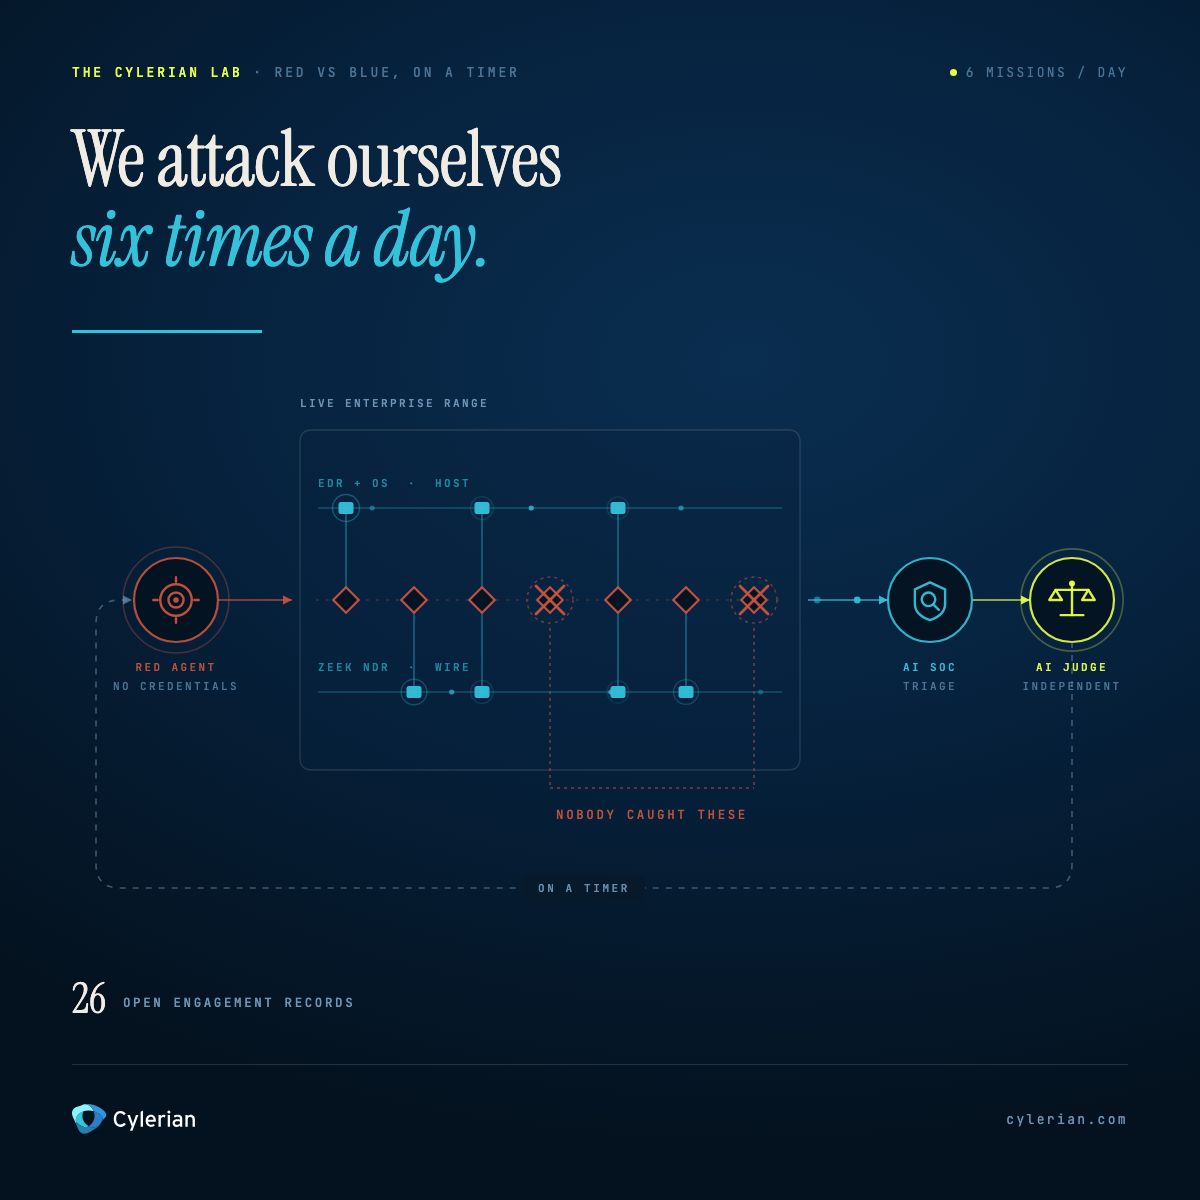
Cylerian releases open-source red team attack datasets for SOC testing
Mission datasets from autonomous AI red team attacks on live enterprise range, with EDR and network telemetry, available for teams to test their own stacks.
Cylerian · 17 Sep 2026 · 1 source · Vendor sources only
Product launch
D3 Security launches Morpheus 2 with graded evidence and narratives
New version adds graded evidence, narrative attack timeline, and defers to analysts when information is missing.
 D3 Security
· 17 Sep 2026 · 1 source · Vendor sources only
Product launch
Imperum introduces Virtus Sentinel for AI security
AI-DER product unifies security across LLMs, AI agents, MCP tools and Shadow AI; includes SDK and OEM-ready engine for vendors.
Imperum · 17 Sep 2026 · 1 source · Vendor sources only
Product launch
Bricklayer AI launches agent-native data plane for enterprise AI agents
The architecture enables persistent, governed access to enterprise-scale data for AI agents.
Bricklayer AI · 16 Sep 2026 · 2 sources · Vendor sources only
Product launch
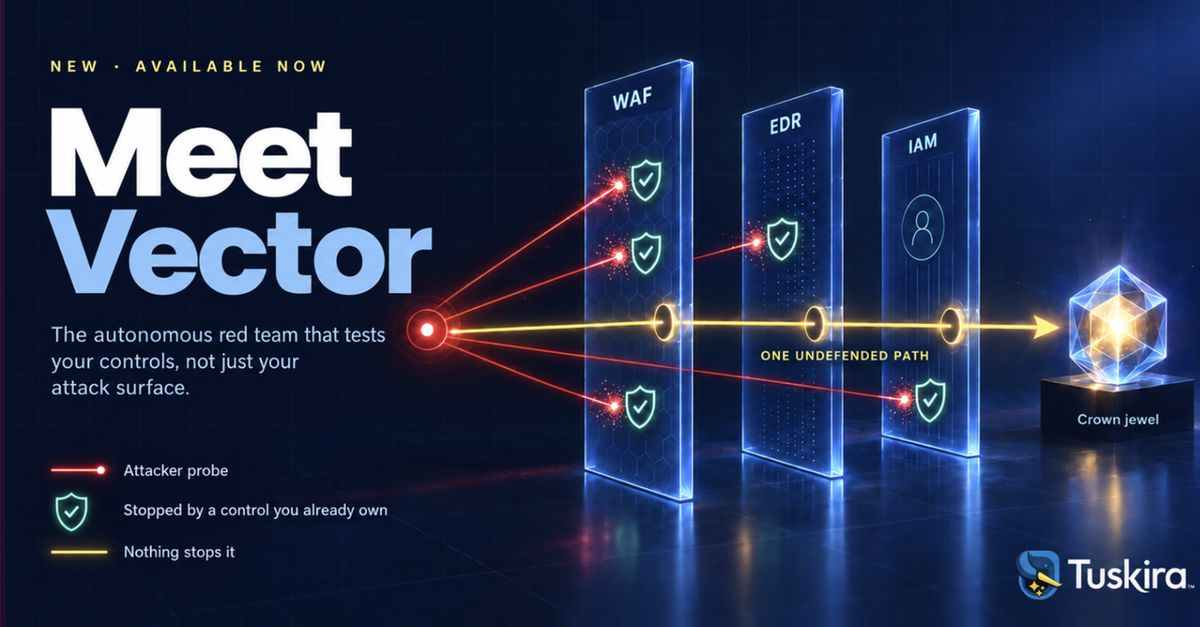
Tuskira launched Vector autonomous red team agent for attack surfaces
Vector continuously probes external attack surfaces and validates findings against deployed security controls.
 Tuskira
· 16 Sep 2026 · 2 sources · Vendor sources only
Product launch
Mars Security launches MARS Playbooks for codified investigations
Playbooks run live across SIEM, EDR, identity and cloud environments with version control and run history, powered by federated search.
Mars Security · 16 Sep 2026 · 1 source · Vendor sources only

