Product launch
IBM introduces vLLM-Hook MIA plugin for AI monitoring
New plugin lets developers inspect and modify AI generation processes with minimal delay.
 IBM · 21 Oct 2026 · 1 source · Vendor sources only
Source: the company's website
New products, and expansions of existing ones. 83 in the period.
New products, and expansions of existing ones.
New plugin lets developers inspect and modify AI generation processes with minimal delay.
IBM · 21 Oct 2026 · 1 source · Vendor sources onlyAdds improved large file uploads, redesigned Organization Dashboard, relay-aware deployment links, and faster Investigation Hub data transfers.
 Binalyze · 20 Oct 2026 · 1 source · Vendor sources only
Enables reliable, cost-effective serving of large AI models on enterprise infrastructure.
IBM · 20 Oct 2026 · 1 source · Vendor sources onlyUnifies threat hunting, detection engineering, insider risk, and alert triage in AI workflows.
 Nebulock · 20 Oct 2026 · 1 source · Vendor sources only
Cantina announced apex-flash-1 model two weeks ago and added Clarion chat, Apex Connection Panel, and Amazon Inspector result categorization.
 Cantina · 19 Oct 2026 · 1 source · Vendor sources only

Co-Hunter Instructions let users set standing rules for data sources, workflows, vocabulary applied to every hunt.
 Mars Security · 19 Oct 2026 · 1 source · Vendor sources only
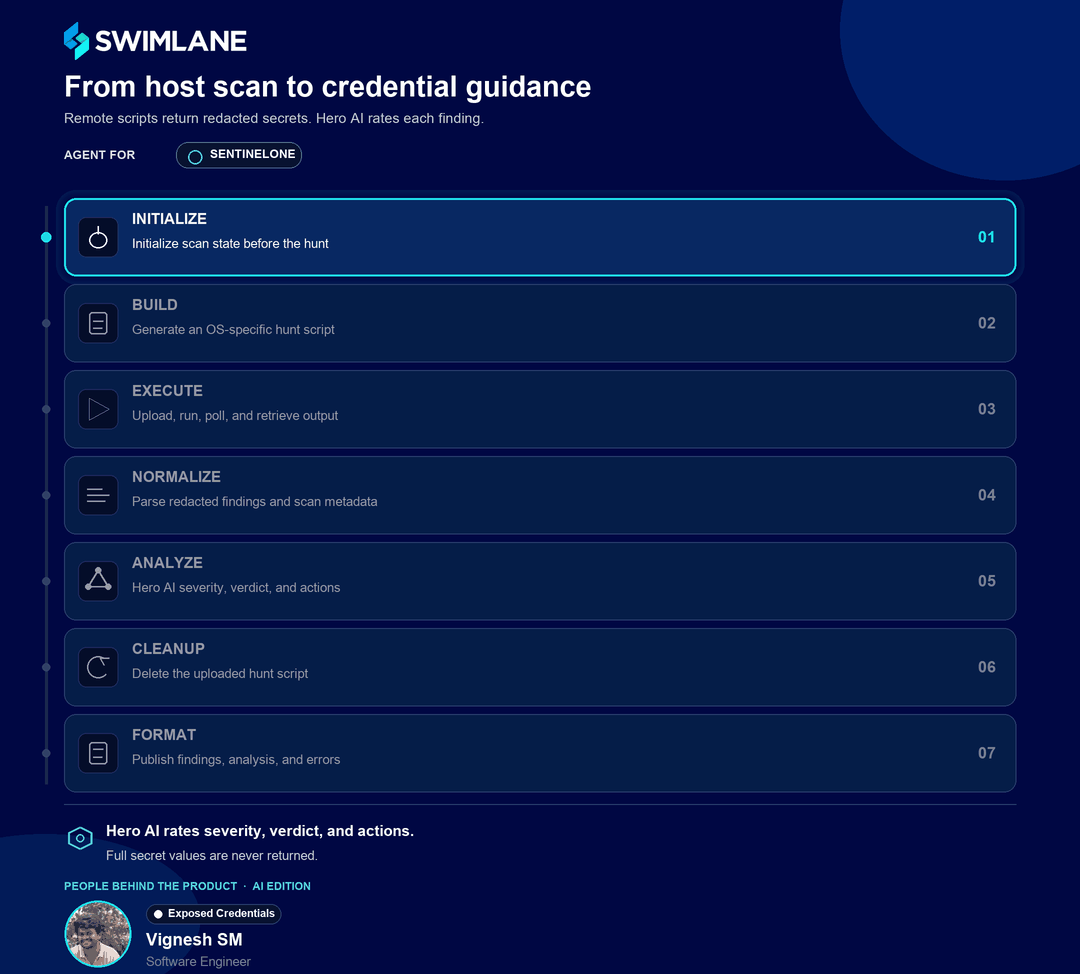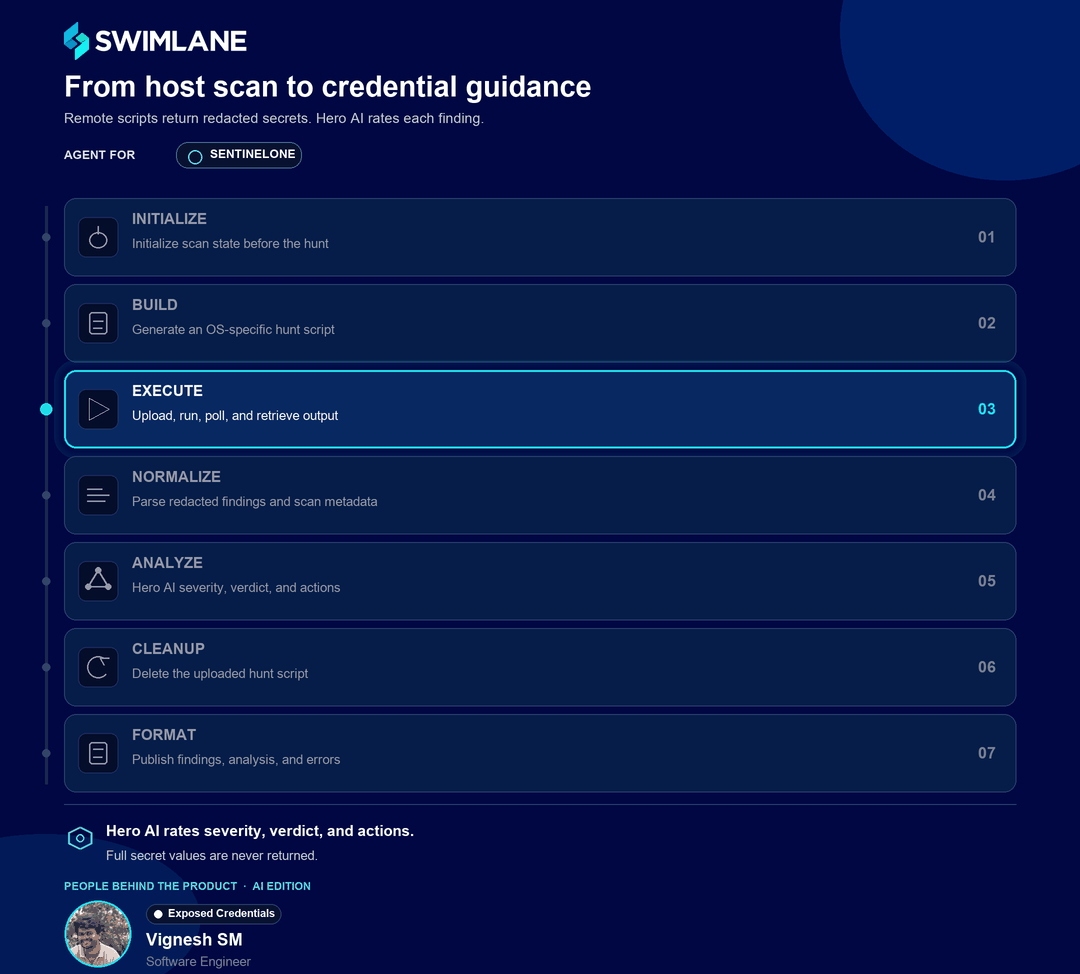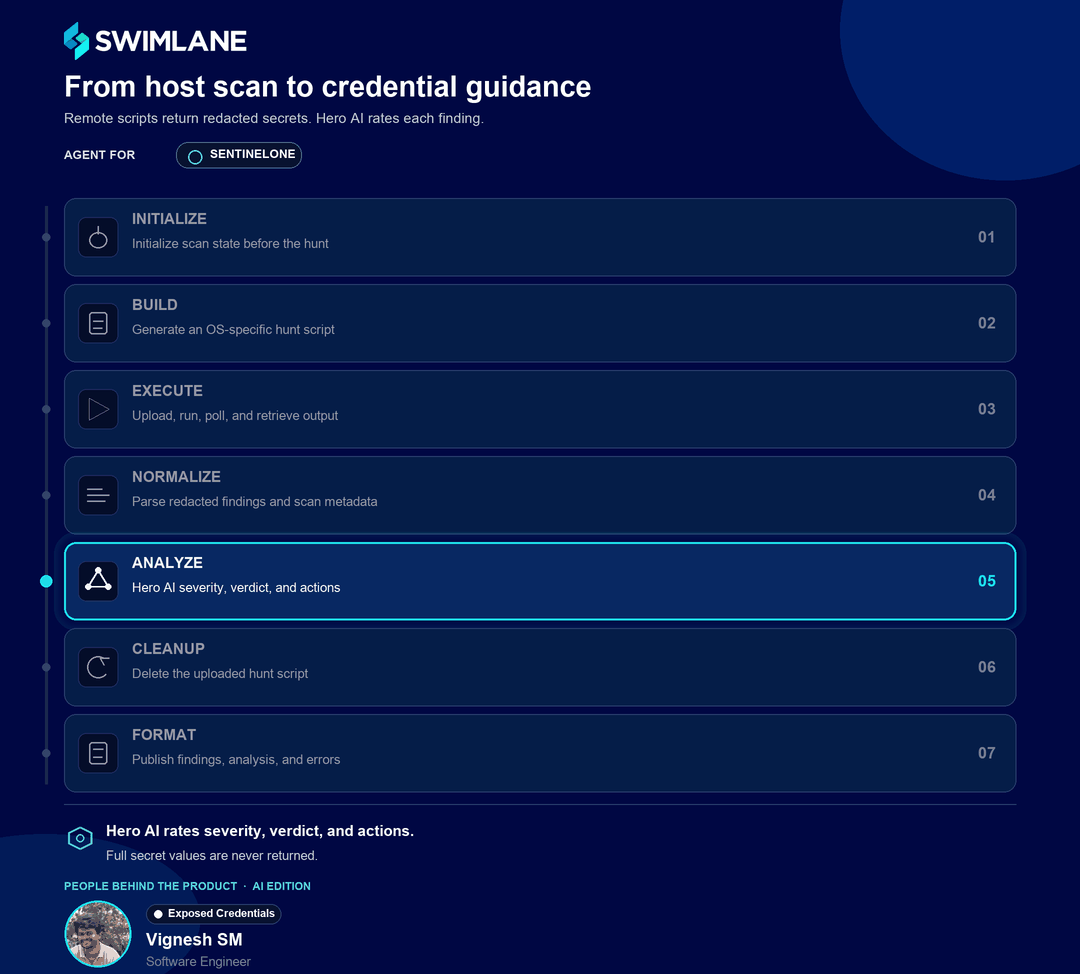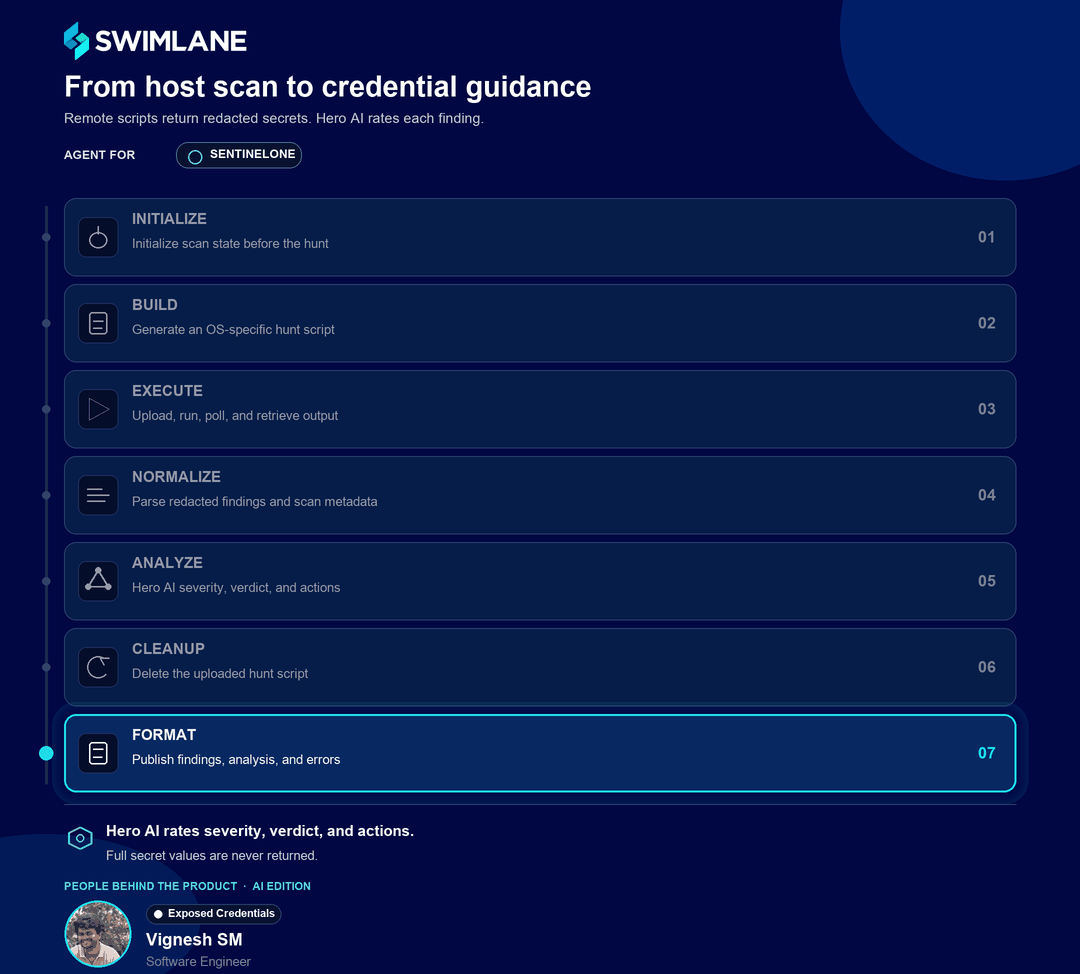
The agent hunts exposed credentials on SentinelOne-managed endpoints, uses Hero AI for triage, and runs deterministically without exposing secrets.
 Swimlane · 16 Oct 2026 · 1 source · Vendor sources only

Detection rules integrate into customer GitHub, GitLab, Bitbucket Cloud, or Cursor Origin repositories via automated pull requests.
 Artemis Security · 15 Oct 2026 · 2 sources · Vendor sources only

Free access to agentic orchestration platform for student-run SOCs, cyber labs and classrooms with pre-built L1, L2, Forensic and SOC Manager agents.
Trellix launched Trellix Wise for Private Cloud, the first on-premises federated AI core for security operations centers, designed to deliver machine-speed cyber defense for data-sensitive environments.
 Trellix · 14 Oct 2026 · 5 sources · Reported by multiple independent sources
SwarmView gives customers visibility into AI-driven investigations, launched at 2026 Security Operations Summit.
 Arctic Wolf · 14 Oct 2026 · 4 sources · Also reported independently

OpenVPN Access Server, Jamf Internet Security, Varonis DatAdvantage, and ThreatLocker integrations added.
 Wirespeed · 14 Oct 2026 · 1 source · Vendor sources only

The platform and Agentic SOC help organizations understand and secure AI decision-making in cyber defense.
Arctic Wolf · 14 Oct 2026 · 2 sources · Vendor sources only
The feature automatically routes security remediation tickets to specific individuals, integrating with Slack, Teams, and Jira.
 Backline AI · 14 Oct 2026 · 2 sources · Vendor sources only
Context Engine provides AI agents enterprise context; nightshift adds AI SRE incident response; AlertZero automates alert triage and threat hunting.
 Elastic · 14 Oct 2026 · 1 source · Vendor sources only

Adds Claude 5 and GPT-6 support, Darktrace connector, deeper Microsoft Sentinel integration, scheduled jobs, exports, and Kubernetes deployment.
 Crogl · 13 Oct 2026 · 1 source · Vendor sources only
Hunt packs let AI threat hunting agents run five to ten hunts simultaneously, giving analysts a head start.
 Dropzone AI · 13 Oct 2026 · 1 source · Vendor sources only
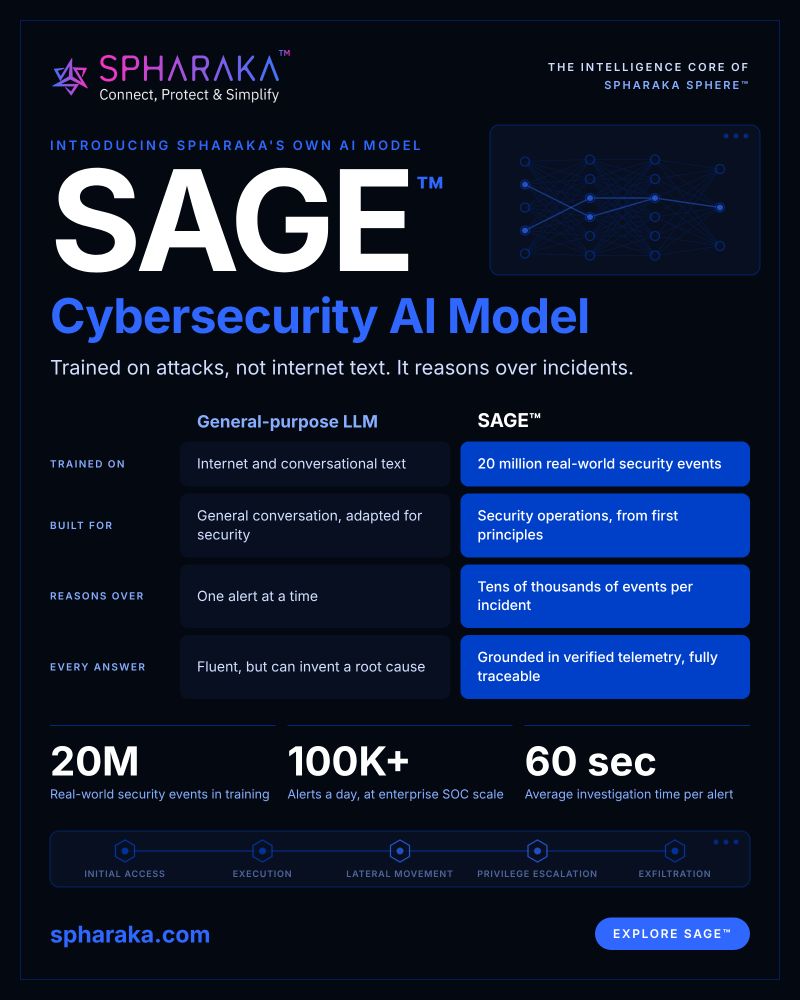
SAGE is trained on 20 million real-world security events and reasons over tens of thousands of events per incident.
 Spharaka · 13 Oct 2026 · 1 source · Vendor sources only

Torq REV offers partners 100% services margin protection, full channel ownership, and a 10-day path to selling.
 Torq · 13 Oct 2026 · 1 source · Vendor sources only

Cotool released new models to its catalog alongside sandbox network restrictions, escalation visibility and delivery resend capability.
 Cotool · 12 Oct 2026 · 1 source · Vendor sources only
Cognitio connects adversary profiles, cross-vendor aliases, MITRE ATT&CK techniques, vulnerabilities and advisories to SOC workflows.
 Imperum · 12 Oct 2026 · 1 source · Vendor sources only
Microsoft announces Azure Maia 200 is now in production, with plans to scale to multi-gigawatt deployments by 2027.
 Microsoft · 12 Oct 2026 · 1 source · Vendor sources only

New release adds governed response, stronger automation and connected security context.
Includes 12 new modules targeting LLMs, Linux privilege escalations, and Windows AARCH64 payloads.
 Rapid7 · 9 Oct 2026 · 1 source · Vendor sources only
The company claims it is top performer on its new Decision-Grade Readiness benchmark measuring trustworthiness of security decisions.
Artemis Security · 8 Oct 2026 · 4 sources · Reported by multiple independent sourcesElastic N.V. launched AlertZero, AI agents for security operations that automate alert triage, threat hunting, and forensic analysis within Elastic Security, with customizable human oversight levels.
Elastic · 8 Oct 2026 · 2 sources · Reported by multiple independent sources
The system enables automated containment of threats like compromised workstations after meeting defined criteria.
 Bricklayer AI · 8 Oct 2026 · 2 sources · Vendor sources only
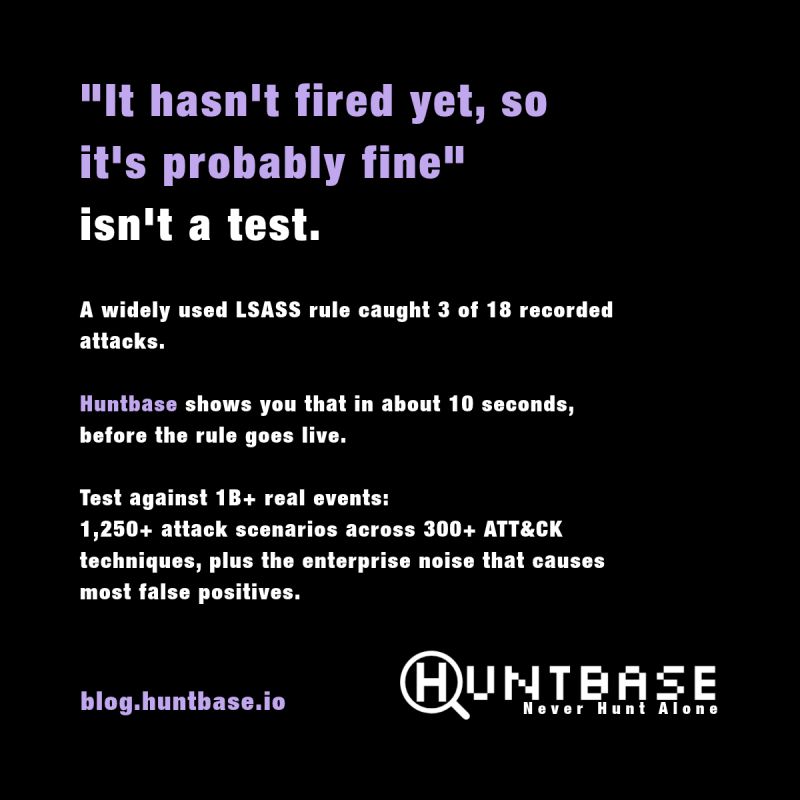
Test lake offers 1,250+ recorded attacks, 300+ MITRE techniques, 1B+ events, rule testing in ~10 seconds.
 Huntbase · 8 Oct 2026 · 2 sources · Vendor sources only
The solution queries data in place and writes AI-generated verdicts back to incidents without SIEM replacement.
 Simbian · 7 Oct 2026 · 1 source · Vendor sources only
AI agents investigate and respond across identity, endpoint, cloud, network, email and SaaS without replacing existing stack.
 NextSOC · 6 Oct 2026 · 1 source · Vendor sources only
Stellar Cyber 7.0 unifies AI-powered case triage, SOC workflows, investigative evidence, automated response and new APIs.
 Stellar Cyber · 5 Oct 2026 · 5 sources · Reported by multiple independent sources

New integrations include Cloudflare WAF, Claroty xDome Healthcare and Industrial, ExtraHop, Imperva WAF, Google Workspace, Veeam, Epic, and 1Password.
Arctic Wolf · 5 Oct 2026 · 1 source · Vendor sources only
The system tracks what changes and why through journals, impact assessments, and full state preservation.
Nebulock · 5 Oct 2026 · 3 sources · Vendor sources only
 CrowdStrike · 5 Oct 2026 · 2 sources · Vendor sources only
Provides direct access to assigned SOC analysts, real-time ticket visibility, and product feedback loop.
 UnderDefense · 5 Oct 2026 · 1 source · Vendor sources only
Intezer reported tripled revenue as enterprises deploy AI security tools in live operations, driven by staffing shortages and SOC alert overload pushing automation adoption.
 Intezer · 2 Oct 2026 · 1 source · Also reported independently
Capabilities help organizations move faster from signal to action with trusted context, governance and automation.
Built on Metasploit and Labs foundation, it monitors threats in real time.
Rapid7 · 2 Oct 2026 · 1 source · Vendor sources only
Adds AI-assisted investigation, agent activity visibility, improved reporting and governance with behavioral baselines.
 Exabeam · 1 Oct 2026 · 8 sources · Reported by multiple independent sources
Update addresses autonomous digital workers using legitimate credentials and faster threat investigation.
Exabeam · 1 Oct 2026 · 3 sources · Also reported independentlyFeatures autonomous response capabilities with AI SRE.
 Palo Alto Networks · 1 Oct 2026 · 2 sources · Vendor sources only

Cyra builds client reports and executes scoped actions like isolation or credential reset through conversational sessions.
 Cylerian · 1 Oct 2026 · 1 source · Vendor sources only
SAGE and AuraXP agents run fully air-gapped with 60-120 second investigations.
Spharaka · 1 Oct 2026 · 1 source · Vendor sources only
New versions bring more ways to analyze data where it lives, put AI assistance into investigations and simplify platform operations.
Enables organizations to retain SIEM data lake while offering AI SOC capabilities, with on-premise deployment for data sovereignty.
UnderDefense · 30 Sep 2026 · 2 sources · Vendor sources onlyThe graph integrates detections, feeds, alerts and historical decisions to reduce cold-start problems for AI agents.
 Anvilogic · 30 Sep 2026 · 1 source · Vendor sources only
Offers 1M token output limit for engineering, knowledge work and cybersecurity; rolling out to defenders via Fairwind Program.
Self-service threat hunting library with reviewed hunts, growing from 152 to 207 hunts in six days.
Huntbase · 30 Sep 2026 · 1 source · Vendor sources only
Investigates alerts across all connected sources with verdict, MITRE mapping, evidence log; no new pipeline needed.
Mars Security · 30 Sep 2026 · 1 source · Vendor sources only
New version can take action with Agent Mode, find content with Semantic Search, and learn naming conventions with Teach AI.

The integration is available today.
 Beacon Security · 29 Sep 2026 · 1 source · Vendor sources only
The Brain connects identities, devices, repositories and cloud services with operating context and prior investigations.
Cantina · 29 Sep 2026 · 1 source · Vendor sources onlyThe platform became generally available September 29, 2026, enabling data-resident AI capabilities.
IBM · 29 Sep 2026 · 1 source · Vendor sources only
SentinelOne Prompt Security enforces policy on Claude prompts in real time, agentless.
 SentinelOne · 29 Sep 2026 · 1 source · Vendor sources only
Agents can now query Fleet and use Azure CLI, with expanded /hunt-intel commands and per-repository GitHub App routing.
Cotool · 28 Sep 2026 · 1 source · Vendor sources only
Nebulock's GATES Method, built with its detection team, helps decide when to promote threat hunts to detections; open source.
Nebulock · 28 Sep 2026 · 2 sources · Vendor sources only
The product autonomously investigates behavioral anomalies and drives governed response across identity, endpoint, cloud, DLP and physical access.
 AiStrike · 28 Sep 2026 · 1 source · Vendor sources onlySentinelOne · 25 Sep 2026 · 1 source · Also reported independently
The platform connects existing tools with AI features for building and scaling solutions.
Microsoft · 25 Sep 2026 · 2 sources · Also reported independently
Exaforce made ExaGo available on the App Store and Google Play.
 Exaforce · 24 Sep 2026 · 2 sources · Vendor sources only
Industry-first appliance for on-prem and air-gapped deployments with local inference, supporting four deployment models including fully air-gapped.
CrowdStrike expands its Falcon platform to secure AI agents, creating new revenue opportunities across endpoint protection, identity management, cloud security, and its agentic security operations center.
CrowdStrike · 23 Sep 2026 · 1 source · Also reported independently
Direct connection brings Sentinel data into agentic security operations for investigations and response.
 BlinkOps · 23 Sep 2026 · 1 source · Vendor sources only
Users can now sign up and run hunts without prior request; platform grew from 149 to 162 hunts.
Huntbase · 22 Sep 2026 · 2 sources · Vendor sources only
Continuously checks every detection against live environment, identifies root cause, and generates customized fixes with human in the loop.
 Spectrum Security · 22 Sep 2026 · 1 source · Vendor sources only

Passive-first platform offers asset discovery, deep packet inspection, and threat detection for 370+ industrial protocols, deployable air-gapped.
Spharaka · 17 Sep 2026 · 1 source · Vendor sources only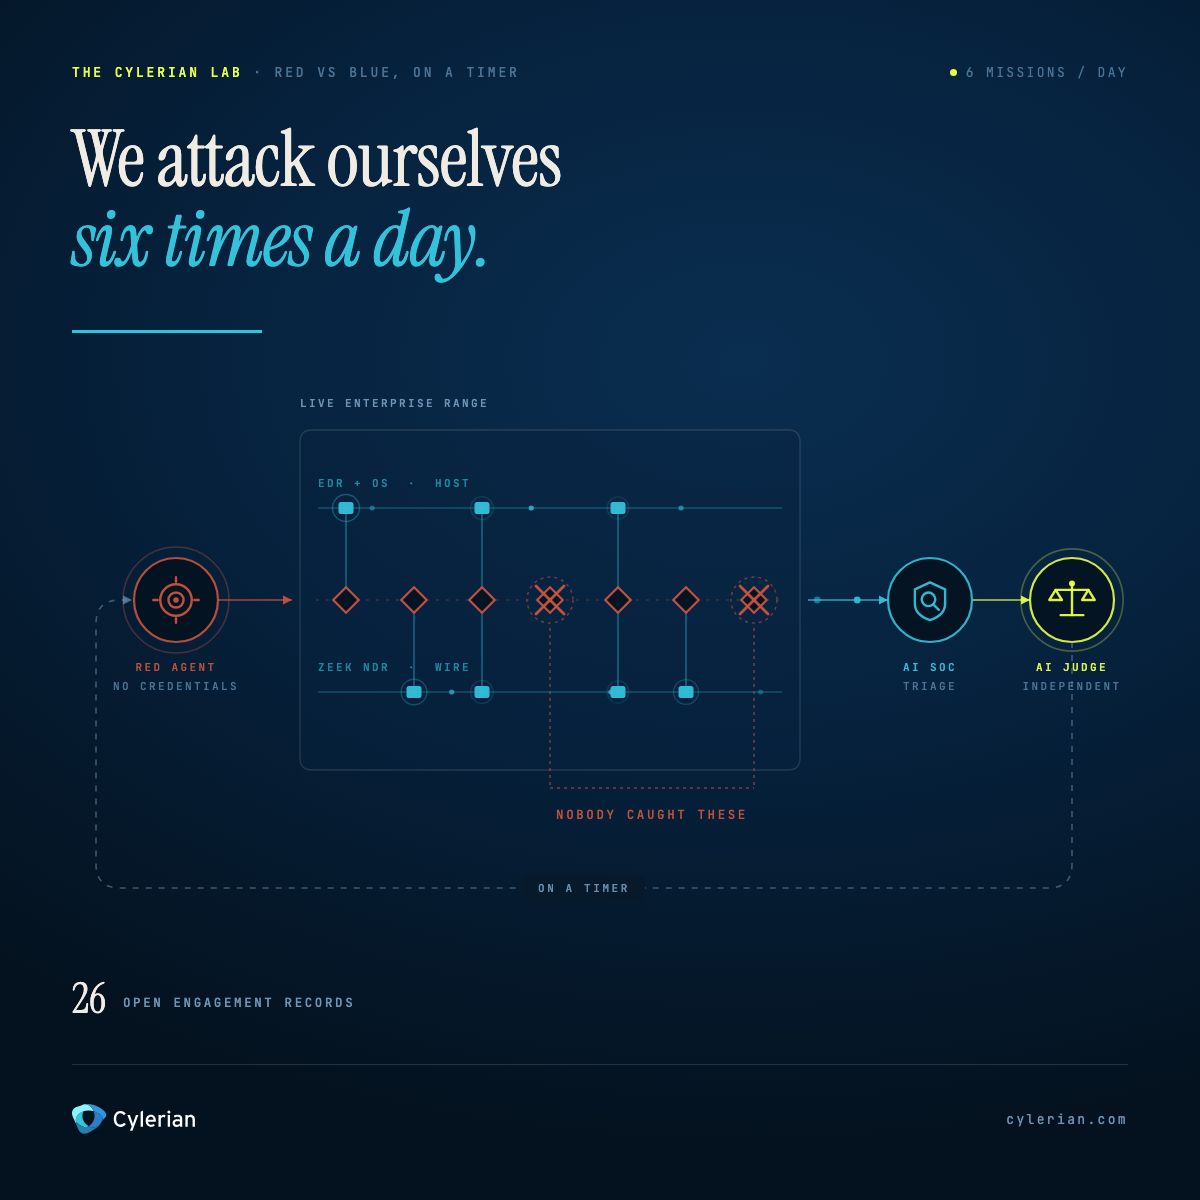
Mission datasets from autonomous AI red team attacks on live enterprise range, with EDR and network telemetry, available for teams to test their own stacks.
Cylerian · 17 Sep 2026 · 1 source · Vendor sources only
The architecture enables persistent, governed access to enterprise-scale data for AI agents.
Bricklayer AI · 16 Sep 2026 · 2 sources · Vendor sources only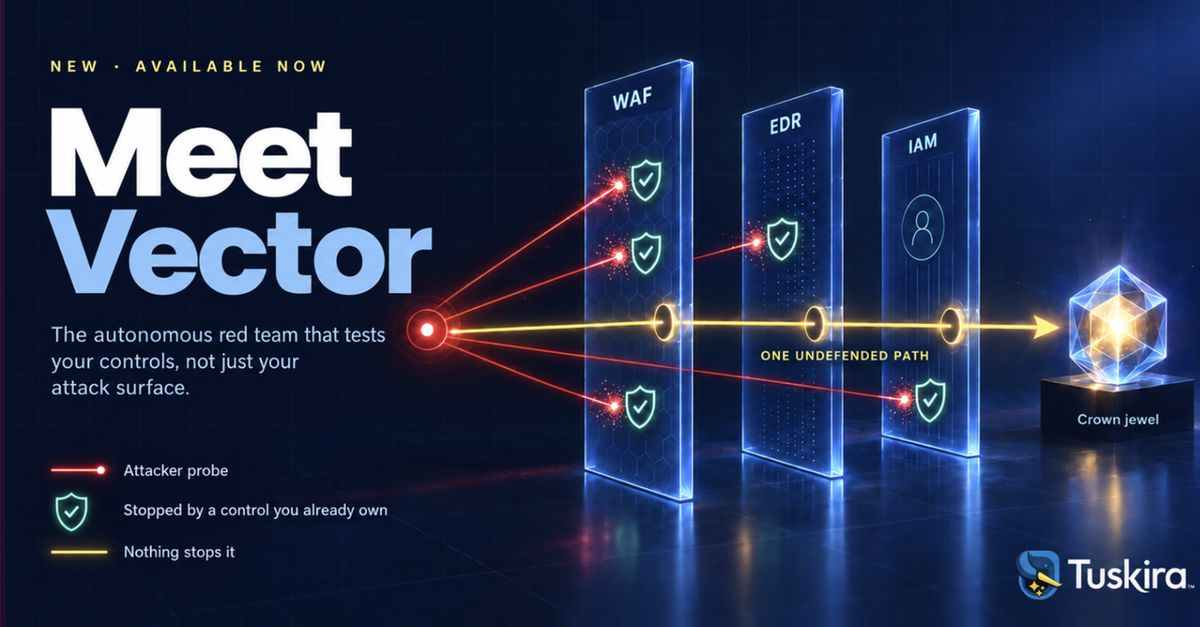
Vector continuously probes external attack surfaces and validates findings against deployed security controls.
 Tuskira · 16 Sep 2026 · 2 sources · Vendor sources only
Playbooks run live across SIEM, EDR, identity and cloud environments with version control and run history, powered by federated search.
Mars Security · 16 Sep 2026 · 1 source · Vendor sources onlySplunk unveiled platform, security and observability enhancements to reposition as a data foundation for the "agentic enterprise," calling it a strategic overhaul rather than routine refresh.
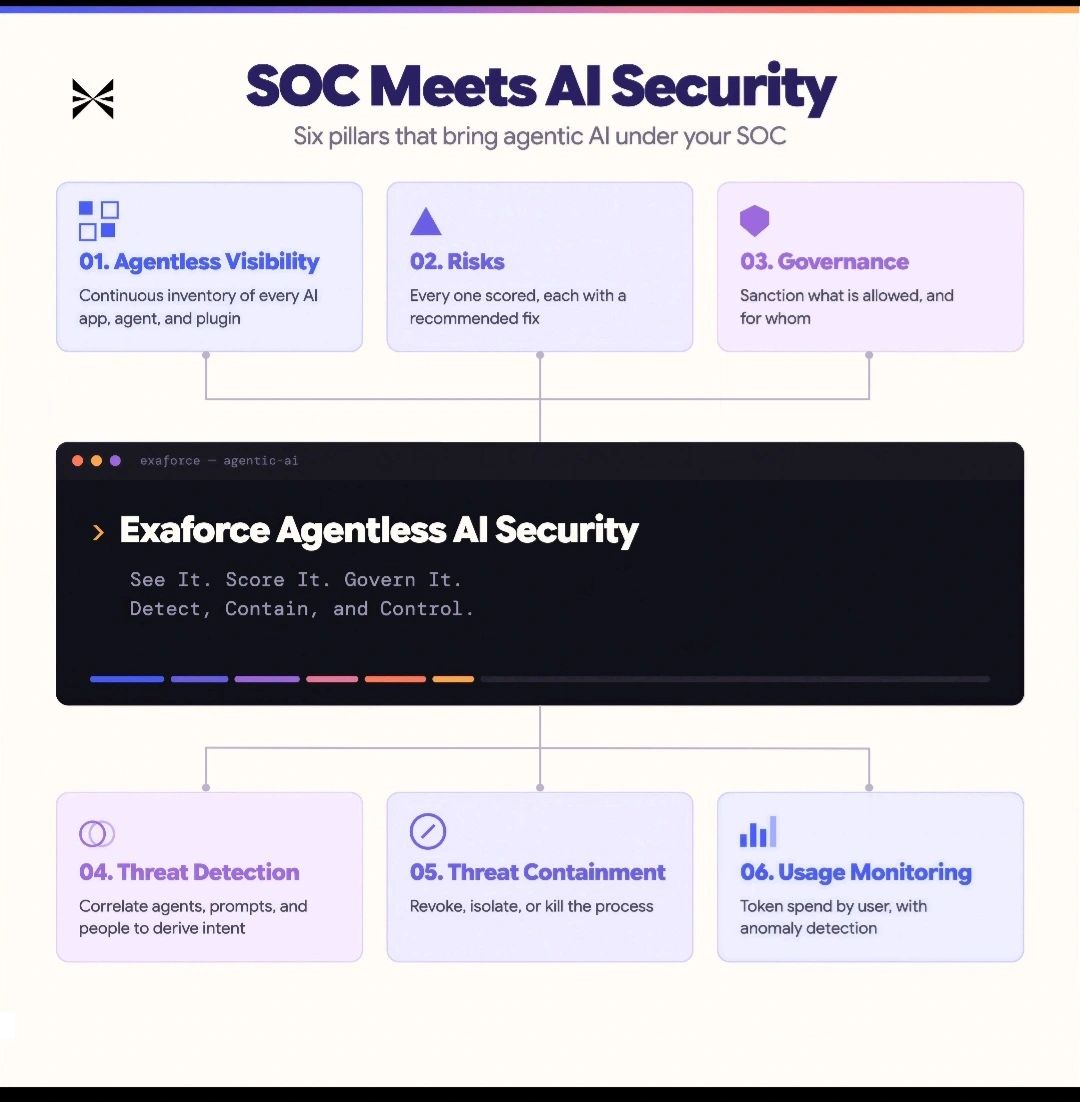
The product discovers AI agents, analyzes risk and permissions, and protects sensitive data across environments.
Exaforce · 15 Sep 2026 · 3 sources · Vendor sources onlyNightwatch automates threat intel processing by triaging reports, hunting telemetry, checking coverage and drafting missing detections.
Cotool shipped Serval and Lumos integrations, redesigned agent editor, automatic Slack setup, and new escalation requirements.
Cotool · 14 Sep 2026 · 1 source · Vendor sources onlyThe capability combines always-on AI, evolved analyst functions, and on-call expert systems.
SentinelOne · 11 Sep 2026 · 1 source · Vendor sources onlyMCP provides tools requiring human expertise to yield craft-quality results.
Bricklayer AI · 9 Sep 2026 · 2 sources · Vendor sources onlyThe engine converts CISA and Mandiant threat advisories into real-time detection capabilities.
Mars Security · 8 Sep 2026 · 2 sources · Also reported independently
Cotool unified Detection and Response workspaces, added model flexibility, hunt thresholds, and Cloudflare/Auth0/1Password/Tailscale integrations.
Cotool · 8 Sep 2026 · 1 source · Vendor sources onlyThe CPU-efficient model learns from analyst dispositions and case outcomes to score alerts before they reach analysts or LLMs.
Imperum · 7 Sep 2026 · 1 source · Vendor sources only
Login Security monitors login activity 24/7 and automatically terminates sessions for high-confidence threats.
Wirespeed · 2 Sep 2026 · 1 source · Vendor sources onlyPortal includes deal registration, platform tour, SPIFF submission, training certification, datasheets, and demo lab for hands-on access.
Intezer · 2 Sep 2026 · 1 source · Vendor sources only
Clarion feature now reads Claude Code telemetry and turns MCP servers into audited and tracked assets.
Cantina · 31 Aug 2026 · 1 source · Vendor sources onlyNew version adds graded evidence, narrative attack timeline, and defers to analysts when information is missing.
 D3 Security · 28 Aug 2026 · 2 sources · Vendor sources only
 By the Cyberfuturists
 made using AunooAI in the SOC · 24 July–22 October 2026 · About · Privacy · Consensus · Three horizons
Send us a story about AI in the SOC that is not here, tell us your company belongs on the list. We read everything; what goes on the page is our call.
Everything here is open to read. If you want the data in your own tools, through our MCP server or an export, ask about data access.
Choosing a product in this market? Advisory helps buyers build a shortlist, test vendor claims and plan a proof of concept.